**Get trusted privacy help today →
80% of health facilities run on fragmented workflows, which raises the odds of mistakes and leaks (Source: MedCore Stats). Your health data is yours. You have the right to see it, fix it, and say who can use it, and laws like HIPAA, GDPR, and India’s DPDP Act 2023 back you up. This beginner guide health care walks you through your rights in plain language so you can protect yourself in 2026 without a law degree.
Think of your medical data like your house keys. You decide who holds a copy, why they have it, and when they must give it back. If keys get lost, you change the locks. The same mindset works here: know what’s private, know your rights, and take simple steps to lock things down.
For a grounded view of how national data-sharing rails work, see this clear, patient-first explainer: your guide to PDS health data systems for 2026. It shows why “who holds your data” matters as much as “who can see it.
What Is Health Care Privacy and Why Should You Care?
Your health information tells a detailed story about you: your diagnoses, lab results, meds, genetic risks, even notes about mood or housing. Health care privacy means you control that story. You choose what to share, with whom, and for what reason. In practice, this is about “PHI,” short for Protected Health Information.
PHI is any data that links health details to you. If a lab report shows your blood sugar and your name, that’s PHI. If the same report has no personal identifiers, it’s not PHI. Simple rule: if it can point back to you and says something about your health, guard it.
Plain examples of PHI (think: your house keys)
- Your ABHA number, insurance policy ID, or medical record number
- Clinic visit notes, diagnoses, allergies, prescriptions, discharge summaries
- Lab values
- Appointment history, bills, and claims tied to your identity
- Messages with your doctor that mention your condition and name
When PHI is breached, real harm can follow. For example, a leaked diagnosis can affect job prospects or lead to social stigma. A stolen insurance ID can fuel false claims. And a “simple” contact leak can trigger phishing calls that trick you into sharing one-time passwords. However, your rights can reduce damage if you act fast: request details of what leaked, demand fixes, and limit future sharing.
In India, two ideas matter a lot in 2026. First, DPDP Act 2023 compliance: organizations must follow clear rules on consent, purpose, and accountability for personal data. Second, India data residency: health systems that keep data in-country make audits and enforcement simpler under Indian law.
Together, they make it easier for you to ask, “Where is my data? Who used it? Prove it.
Tip: Treat access like keys. Only share what’s needed for care. Ask providers to disable accounts you no longer use.
Moreover, this beginner guide health care section is your baseline: know what PHI is, why it’s sensitive, and what a breach looks like. With that, the next step is learning which laws protect you and how to use them.
Also Read!
Your Guide to Understanding PDS Health and Patient Data Systems
How to Choose an EHR Your Way: A Practical Guide to Customizable Electronic Health Records
Key Health Care Privacy Laws You Need to Know — A Step-by-Step Breakdown
Different regions have different rules. But they share a core promise: you can see, fix, and control your data. Below is a simple walkthrough of three major laws. HIPAA (US), the DPDP Act 2023 (India), and GDPR (EU).
HIPAA (United States)
-
Step 1: Who it protects
Patients of “covered entities” like hospitals, clinics, and insurers, plus their business associates. -
Step 2: What it covers
PHI in any form, paper, digital, or spoken. -
Step 3: Your rights
Access your records, get copies, ask for corrections, get an accounting of disclosures, set communication preferences, and file complaints. -
Step 4: Limits and exceptions
Data can be shared for treatment, payment, and health operations. Emergencies and public health needs may allow use without consent.
For a clear, official overview, see this U.S. HHS HIPAA guide.
DPDP Act 2023 (India)
-
Step 1: Who it protects
“Data principals”, that’s you, when an organization processes your personal data, including health data. -
Step 2: What it covers
Digital personal data, with duties on “data fiduciaries” to process it lawfully, with purpose limits and safeguards. -
Step 3: Your rights
Access summaries of your data, correct or erase it, and complain to a grievance officer and, if needed, the Data Protection Board. -
Step 4: India context
Look for DPDP Act 2023 compliance and India data residency in your provider’s policy. Ask who can see audit logs and how consent is recorded.
GDPR (European Union)
-
Step 1: Who it protects
People in the EU whose personal data is processed, even by organizations outside the EU that target EU residents. -
Step 2: What it covers
Personal data in any format. Health data is “special category,” which needs stronger protection. -
Step 3: Your rights
Access, rectification, erasure (“right to be forgotten”), restriction, portability, and objection. You also get clear consent choices. -
Step 4: Cross-border data
Transfers must have safeguards. Controllers must be transparent and keep records of processing.
Read the official GDPR overview from the European Commission.
Standards that connect the dots
Laws set rights, but technical standards make those rights real in clinics. For example, FHIR R4 allows structured, secure data exchange while keeping a clear access trail. And HL7 v2 inbound connections let labs and devices send results into hospital systems without messy copy-paste. When your provider says they support FHIR R4 and HL7 v2 inbound, they’re telling you they can move and log data in a safer, traceable way.
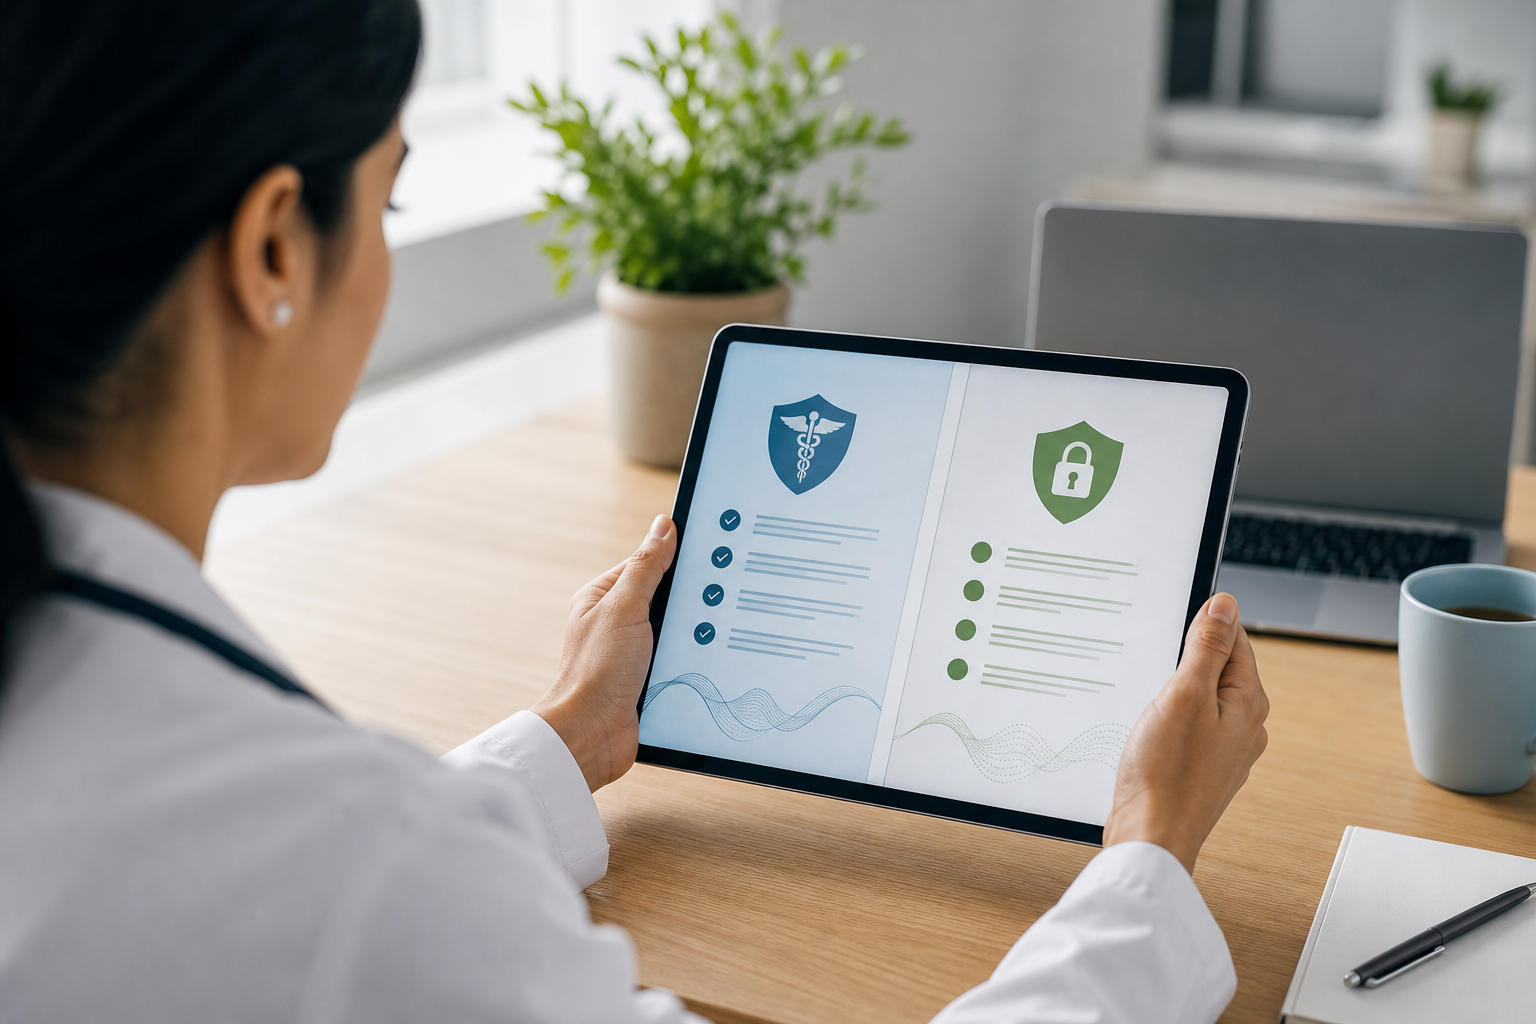 , GDPR; rows: Who Is Protected, What’s Covered, Core Rights, Exceptions; bright, legible icons; modern 2026 design)
As you read this beginner guide health care laws section, notice the common thread: know, access, correct, and control. Different wording, same backbone. Use that pattern as your checklist in 2026, wherever you receive care.
Common Misconceptions About Your Medical Data Privacy
Misinformation makes people give up control too soon. Let’s fix that with quick, clear facts.
-
Myth: “My doctor can share anything with my family.
Reality: No. Without your consent, staff can only share limited info, such as in emergencies or when required by law. -
Myth: “Digital records are less safe than paper.
Reality: Not by default. Encrypted EHRs with role-based access and audit trails beat unlocked filing cabinets. -
Myth: “Privacy laws only matter in the US.
Reality: The EU’s GDPR and India’s DPDP Act 2023 protect millions. Your rights depend on where care happens and who processes your data. -
Myth: “Small clinics don’t need to comply.
Reality: Size doesn’t erase duties. Patients still have rights to access and corrections, and clinics still need consent and security basics. -
Myth: “Interoperability means anyone can see my record.
Reality: Interoperability (e.g., FHIR R4) moves data with controls. It should include consent logs and audit trails, not open doors.
“We replaced three tools with MedCore. Billing, pharmacy and lab now talk to each other without exports.” — Ravi Prasad, Administrator, Sunrise Clinic
Moreover, the market gap is real: 75% of the market is underserved by existing tech, and 80% of facilities rely on fragmented workflows (MedCore Stats). Fragmentation breeds risk: lost faxes, unreadable scans, and missing consents. However, unified systems reduce “hand-off” errors and make your requests, “Show me who accessed my record last week”, practical and fast.
If this beginner guide health care myth-busting teaches you one habit, make it this: ask “How do you log access, and can I see it?” A confident, privacy-aware provider will have a clear answer.
For broader context on national data rails and how they affect consent, see this patient-friendly PDS health data systems overview. It connects policy to real clinic workflows.
Also Read!
Your Guide to Appointment Plus: What It Is, How It Works, and the Best Alternatives
Tools and Systems That Help Protect Health Care Privacy
Good privacy is not only a policy; it’s also the right stack. Four categories matter most: encrypted EHR systems, consent management platforms, audit trail software, and secure messaging tools.
First, encrypted EHRs act like a locked vault. Look for end-to-end encryption, at rest and in transit, with role-based access. Moreover, insist on clear audit logs: who opened your chart, when, and what they viewed. Second, consent management platforms should record purpose (why data is used), scope (which data), and expiry.
You should be able to withdraw consent and see proof that access changed. Third, audit trail software needs tamper-evident logs and alerts. If a pharmacy clerk opens a VIP patient’s file without cause, alarms should ring. Fourth, secure messaging should support patient-safe defaults: verified sender, minimal PHI in the body, and links that expire.
Features to look for (beyond the brochure)
- DPDP Act 2023 compliance and India data residency options for clinics in India
- Standards-based exchange: FHIR R4 and HL7 v2 inbound to cut risky copy-paste
- Role-based access and least-privilege defaults for all staff
- Full audit trail with patient-facing access reports
- Strong encryption, plus offboarding workflows that remove stale access
Tools like MedCore are one option if your clinic wants a unified EHR with FHIR R4 support, HL7 v2 inbound connectivity, DPDP Act 2023 compliance, and India data residency. In practice, that means fewer exports, fewer hand-offs, and clearer audit trails. Security signals also matter: 24/7 uptime, DLT-compliant SMS for alerts, and structured EHR modules across vitals, allergies, and problem lists (MedCore Features and Stats). That said, choose the tool that fits your care setting; ask for a live demo and proof of the above features.
Furthermore, this beginner guide health care tools section is a reminder: technology should make your rights easy to use. If a tool can’t show you who opened your record, it’s not private, it’s opaque.
**See secure pricing now →
What to Do Next — Protecting Your Health Data Starting Today
Big change starts with small, clear steps. Use this five-step plan and repeat it at each clinic or hospital you visit in 2026.
-
Request your records
Ask for a copy of your record and your last 12 months of access logs. Note any errors to fix. -
Check encryption and access controls
Ask: “Is my data encrypted at rest and in transit? Do you use role-based access?” Write down the answers. -
Review consent forms
Before you sign, look for purpose, scope, and expiry. Cross out blanket language or ask for a narrower purpose if needed. -
Confirm legal compliance
In India, ask about DPDP Act 2023 compliance and India data residency. In the US or EU, ask how HIPAA or GDPR rights are honored. -
Set alerts and reduce exposure
Enable patient-app alerts for new results or access. Share data only when needed. Disable old logins.
Moreover, bookmark this beginner guide health care action plan. Reuse it with each provider. Over time, these small moves add up to real control.
Key Takeaways
- Your PHI is like house keys: share on purpose, and change locks after a breach.
- Core rights repeat across laws: access, correct, and control your data use.
- Ask providers for encryption, role-based access, FHIR R4, and audit trails.
- In India, DPDP Act 2023 and India data residency shape real-world safeguards.
- Unified systems cut risk; fragmented tools fuel errors and missing consents.
What to Do This Week
Today, request your latest medical record and an access log from one provider. This week, review your consent forms and ask how encryption and audit trails work. If your clinic wants help choosing privacy-first tools, book a short conversation.
Moreover, if you’re researching how national data backbones affect your day-to-day care, read the in-depth PDS health data systems guide for 2026. It ties policy choices to real clinic workflows that touch your records every day.
“Our OPD wait time dropped from 40 minutes to 12. The live token display alone was worth the switch.” — Dr. Meera Rao, Medical Director, Asha Hospital
Finally, remember this beginner guide health care message: your rights work best when you use them. Ask questions, keep notes, and expect proof.